MANUFACTURING CYBERSECURITY RESEARCH
Manufacturing Identity Security: Key Findings from 21 Manufacturers
Accent Consulting analyzed 1,625 anonymized cybersecurity findings from 21 manufacturing organizations between 2023 and 2026. The research identifies common identity and access risks affecting employees, contractors, vendors, shift workers, administrators and remote users.
What is Manufacturing Identity Security?
Manufacturing identity security protects access for employees, contractors, vendors, administrators, service accounts, and remote users across business, engineering, cloud and operational technology systems.
It includes strong authentication, user access reviews, password controls, vendor access, privileged accounts, remote connections, and account removal when access is no longer needed.
Why Does It Matter?
Manufacturing environments connect people, applications, machines, production systems, and business tools. As a result, a compromised or poorly managed account may provide access to sensitive information or systems that support production.
Strong identity controls help manufacturers limit unnecessary access, protect critical systems, and reduce the impact of compromised accounts. In addition, strong authentication helps verify users before they access important systems.
How Identity Risk Can Affect Manufacturing Operations
Manufacturing environments connect people, applications, machines, and production systems. For example, employees need access to facilities, while engineers may require remote access to support equipment.
However, every account can introduce risk. Weak passwords, excessive permissions, and unmanaged vendor access may expose critical systems. As a result, attackers could gain access to sensitive data or disrupt production.
Our research identified several identity-related weaknesses across the manufacturers we assessed. These included exposed credentials, access permissions, account management, and privileged access.
Therefore, identity security is more than an IT concern. It also plays an essential role in protecting production, sensitive information, and daily business operations.
54%
of identified issues were identity-related
877
credentials were identified in the research.
201
non-expiring passwords were identified.
78
credentials were exposed on the dark web.
Accent Consulting analysis of 1,625 anonymized findings from 21 manufacturing organizations, 2023–2026. Explore the full manufacturing cybersecurity research to review the other recurring risk areas.
IDENTITY RISK OVERVIEW
Identity Security Is an Operational Risk
In manufacturing, identity security protects more than usernames and passwords. It also helps secure the systems and processes that keep production running, including engineering applications, production systems, remote-support tools, and operational technology.
For example, engineers may need access to production applications. Meanwhile, vendors may require remote connections to service equipment. If attackers compromise those accounts, they could reach sensitive information or disrupt operations.
The potential impact depends on each account’s permissions and the systems it can access. In particular, privileged accounts, which have broader permissions, can create greater risk.
For this reason, manufacturers need to know who has access, what each account can reach, and whether that access remains necessary. Strong identity controls help teams protect critical systems while keeping essential work moving.
WHAT THE DATA SHOWED
What Our Research Revealed About Manufacturing Identity Security
Identity-related findings accounted for 54% of the cybersecurity issues identified in the research sample. The analysis also identified 877 credentials, including 201 non-expiring passwords and 78 credentials exposed on the dark web.
These results highlight several areas that deserve attention. Manufacturers should review password policies, account permissions, and privileged access. Furthermore, they should check how employees, contractors, and vendors connect to business systems.
Manufacturers should also review how employees, contractors, and vendors connect to business systems. For example, remote access should be limited to approved users, protected with strong authentication, and reviewed regularly.
Ultimately, manufacturers need to protect the accounts that connect people to production systems, sensitive data, and critical business applications.
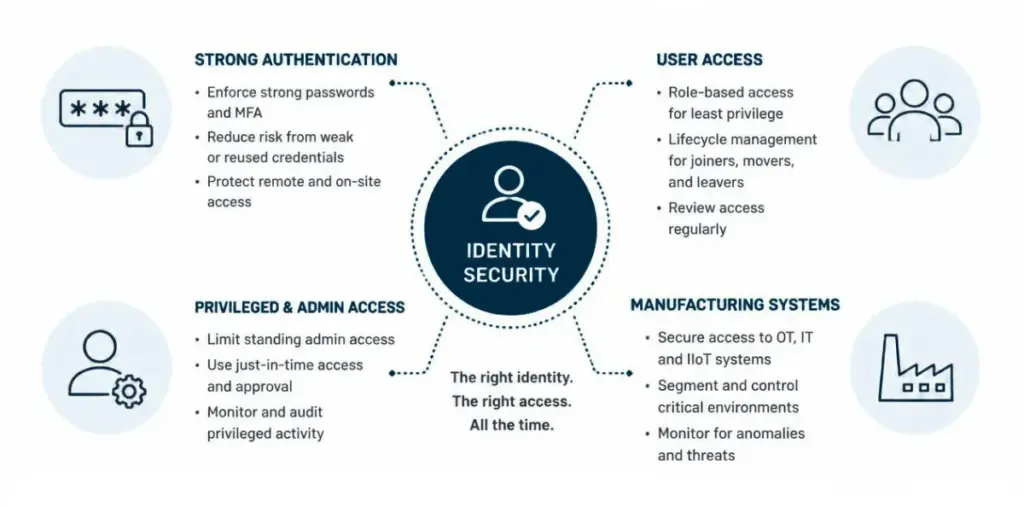
Four Foundations of Manufacturing Identity Security
Effective identity security starts with four core practices. Together, these practices help manufacturers control access, protect accounts, and secure connected systems.
WHAT LEADERS SHOULD DO NEXT
Where Manufacturers Should Start
Manufacturers do not need to solve every identity security issue at once. Instead, they should focus on the accounts and systems that create the greatest risk.
1. Review Current Access
Start by reviewing employee, contractor, vendor and service accounts. Then identify inactive accounts, excessive permissions, and remote access tools. Finally, remove access that users no longer need.
2. Protect High-Risk Accounts
Next, strengthen authentication for administrator accounts and remote connections. Require MFA wherever appropriate, eliminate unnecessary shared accounts, and review password policies.
3. Protect High-Risk Accounts
Finally, establish a regular access review process. In addition, monitor unusual activity and remove accounts when employees or vendors leave. Review permissions whenever job responsibilities change.
Together, these steps provide a practical starting point. Manufacturers can address the most important gaps first and improve identity security over time.
IDENTITY SECURITY FRAMEWORK
Why Identity Risk Persists in Manufacturing
Identity risks often grow over time. For example, employees change roles, contractors finish projects, and vendors receive temporary access. Without regular reviews, these accounts may retain permissions they no longer need.
How Changing Roles Creates Access Gaps
Manufacturing environments often include shared workstations, multiple shifts, legacy systems, and remote support tools. Consequently, access requirements can change quickly.
Consider a contractor who needs temporary access to repair equipment. If the team never removes that access, the account may remain active long after the work ends.
Why Excessive Permissions Increase Risk
Over time, accounts can accumulate unnecessary permissions. Inactive accounts, exposed credentials, and poorly controlled administrator access can create additional weaknesses.
Therefore, manufacturers should regularly review who has access, what users can reach, and when that access should end. These reviews help teams close gaps before attackers exploit them.
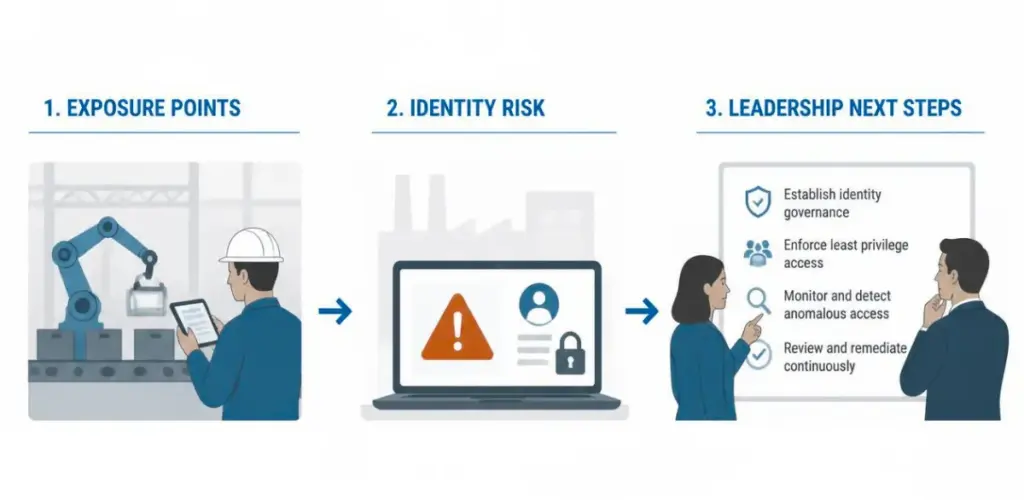
How Identity Risk Builds
Identity risk often follows a predictable pattern. First, exposure creates opportunities for attackers. Next, weak controls increase the danger. Finally, leadership decisions shape the response.
TURN INSIGHTS INTO ACTON
How Manufacturers Can Strengthen Identity Security
Why is identity security important in manufacturing?
Identity security helps protect production systems, business applications, and sensitive data. If attackers compromise an account, they may gain access to systems that support daily operations. For that reason, manufacturers should protect user accounts, limit administrative access, require MFA, and review permissions regularly.
What are the biggest identity challenges in manufacturing
Common challenges include shared accounts, excessive permissions, inactive users, weak passwords, limited MFA coverage, and vendor access that remains active longer than necessary. Older production systems may also make identity controls more difficult to apply. However, manufacturers can reduce risk by prioritizing critical accounts, documenting access, and reviewing permissions regularly.
Why are credentials and passwords still a major risk?
Stolen or reused credentials can allow attackers to bypass other security controls. Once an account is compromised, attackers may use it to access business applications, remote-access tools, production systems or sensitive information. Manufacturers should use MFA, strong password policies, password managers, account monitoring and prompt removal of unused credentials.
How should manufacturers manage vendor access securely?
Manufacturers should provide vendors with only the access they need, for only as long as they need it. Vendor accounts should use MFA, limited permissions, approved access methods, and activity monitoring. In addition, organizations should assign an owner to each vendor connection and remove access when maintenance or support work is complete.
What are the best practices for managing identity security?
Effective identity security begins with an accurate inventory of users, accounts, roles, and permissions. Manufacturers should prioritize MFA, protect administrative accounts, remove inactive users, limit access based on job responsibilities, review vendor permissions, monitor account activity, and regularly test access controls. Together, these steps help reduce unauthorized access to business and manufacturing systems.
LEADERSHIP NEXT STEPS
Close the Identity Gaps that Matter Most.
Prioritize password controls, administrative-account protection, MFA, vendor access, and regular permission reviews across your organization.
Accent Consulting can help your organization identify identity weaknesses and build a practical plan to protect accounts, systems, and manufacturing operations.