MANUFACTURING CYBERSECURITY RESEARCH
The Encryption Gap: How Manufacturers Can Protect Sensitive Data
Manufacturers move sensitive data across devices, removable media, cloud systems, wireless networks and business applications. Without proper encryption and access controls, that data may become exposed. Accent Consulting analyzed 1,625 anonymized cybersecurity findings from 21 manufacturing organizations between 2023 and 2026. The research found recurring encryption and data-protection gaps that may affect confidentiality, operations and regulatory readiness.
What Is Data Encryption in Manufacturing?
Data encryption changes readable information into a protected format. Only approved users, devices or systems with the right key can read it.
Manufacturers use encryption to protect data on devices, in storage, and across networks. For example, this data may include engineering files, production records, customer information, financial data, employee records, passwords, cloud data, removable drives, and wireless connections.
As a result, encryption helps reduce the damage caused by a lost device, stolen file, or unauthorized connection.
Why Does Encryption Matter in Manufacturing?
Encryption helps protect data when someone loses a device, gains access without permission, or captures data moving across a network.
However, encryption works best when teams use it with other security controls. Manufactures should also use strong passwords, MFA, secure settings, limited access, monitoring and regular reviews.
Together, these controls help protect sensitive information as it moves through business and production environments.
Why Manufacturing Data Exposure Often Starts Quietly
Manufacturing leaders may not notice a data problem at first. Instead, they may discover it after a device goes missing, a system fails, or an attacker gains access.
For example, a laptop may not use encryption. A cloud folder may allow access to too many users. A removable drive may contain engineering files. Also, a wireless network may send data without enough protection.
In addition, a wireless network may send data without enough security. Each issue may seem small on its own. However, several small gaps can expose sensitive information.
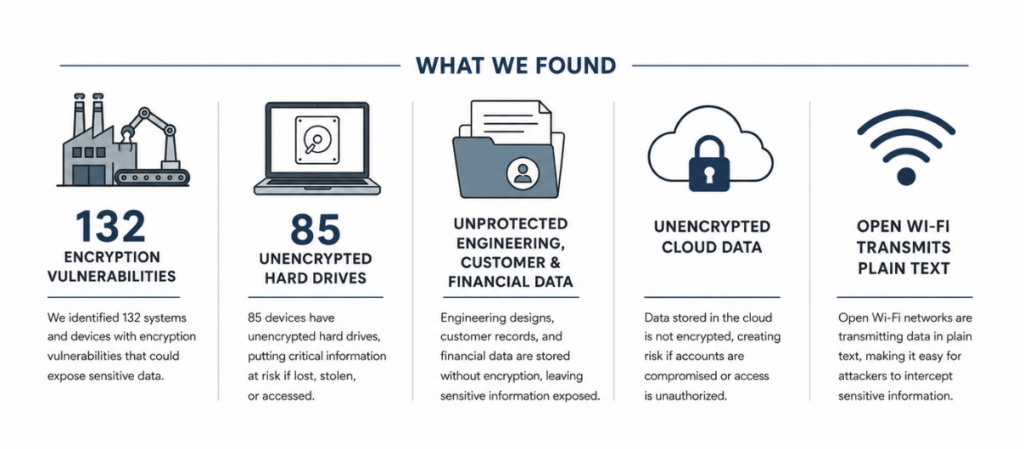
Accent Consulting analyzed 1,625 anonymized cybersecurity findings from 21 manufacturing organizations. The research found 132 encryption-related findings and 85 unencrypted hard drives.
These findings do not mean that an attacker stole or accessed the data. Instead, they show that some data may not have had the level of protection expected in the assessed environments.
For manufacturers, the concern is more than a technical problem. Engineering files, process details, pricing information, customer data, employee records, and business information can all affect the value and strength of the company. Explore the full manufacturing cybersecurity research to review the other risk areas.
21
manufacturing organizations assessed.
8%
of identified findings were encryption-related.
132
encryption-related findings identified.
85
unencrypted hard drives identified.
Source: Accent Consulting analysis of 1,625 anonymized cybersecurity findings from assessments of 21 manufacturing organizations conducted between 2023 and 2026.
OPERATIONAL IMPACT
How Encryption Gaps Can Affect Manufacturing Operations
Manufacturing data can exist on laptops, servers, cloud systems, removable drives, wireless networks, production systems, and business applications.
Because data moves through many places, its protection may not be the same everywhere.
For example, a lost laptop or removable drive may contain readable engineering files, customer records, financial information, or employee data. In the same way, a cloud folder with weak settings may allow people to view information they do not need.
The impact may go beyond data privacy. Exposed information can affect company secrets, production work, customer trust, business advantage, and legal or contract needs.
For that reason, manufacturers should review encryption along with identity security, access controls, cloud settings, remote access, and data-retention rules.
KEY FINDINGS
What the Encryption Findings Reveal
The findings point to a broader pattern: sensitive data may exist across many ordinary systems and environments.
The research identified encryption-related findings involving hard drives, cloud storage, engineering information, customer data, financial information, and wireless communications.
For example, an unencrypted hard drive may contain information that remains readable if the device is lost or removed from service. Similarly, an improperly protected cloud repository may expose information to users who do not need access.
The risk depends on the type of data, where it is stored, who can reach it, and whether encryption protects it during storage and transmission.
Therefore, manufacturers should identify where sensitive data exists, classify its importance, and confirm that appropriate encryption and access controls are in place.
BUSINESS IMPACT
Business Impact of Stronger Data Protection
Strong data-protection practices can reduce the likelihood and impact of unauthorized disclosure. They may also help manufacturers:
- protect engineering files and intellectual property;
- reduce exposure from lost or retired hardware;
- protect customer and employee information;
- limit the impact of credential theft;
- support privacy, contractual, and regulatory obligations; and
- improve confidence in business continuity and operational resilience.
The source material also points to broader business consequences when encryption is missing. These may include intellectual-property exposure, legal or regulatory concerns, customer trust issues, insurance implications, and delays in responding to an incident.
However, encryption does not stop every type of unauthorized access. It should work with strong passwords and MFA, limited access, secure settings, system monitoring, and response plans.
RISK LOCATIONS
Where the Encryption Gap Appears
Encryption gaps can appear in everyday systems and workflows. These may include endpoint devices, shared cloud repositories, removable media, wireless networks, production systems, and business applications.
Accent Consulting’s findings point to three common exposure areas:
- Unencrypted hard drives: 85 unprotected drives contained engineering files, customer data and financial records.
- Cloud storage without encryption: Personally identifiable information, including employee and customer records, was stored in cloud environments without enough protection.
- Plaintext data on open Wi-Fi: Information transmitted over open wireless networks was visible to anyone on the network.
Each issue creates a similar business concern: sensitive manufacturing information may remain readable outside its intended controls.
Manufacturers should therefore review where sensitive data is stored, how it moves between systems, and which users or devices can access it.
Where the Encryption Gap Appears
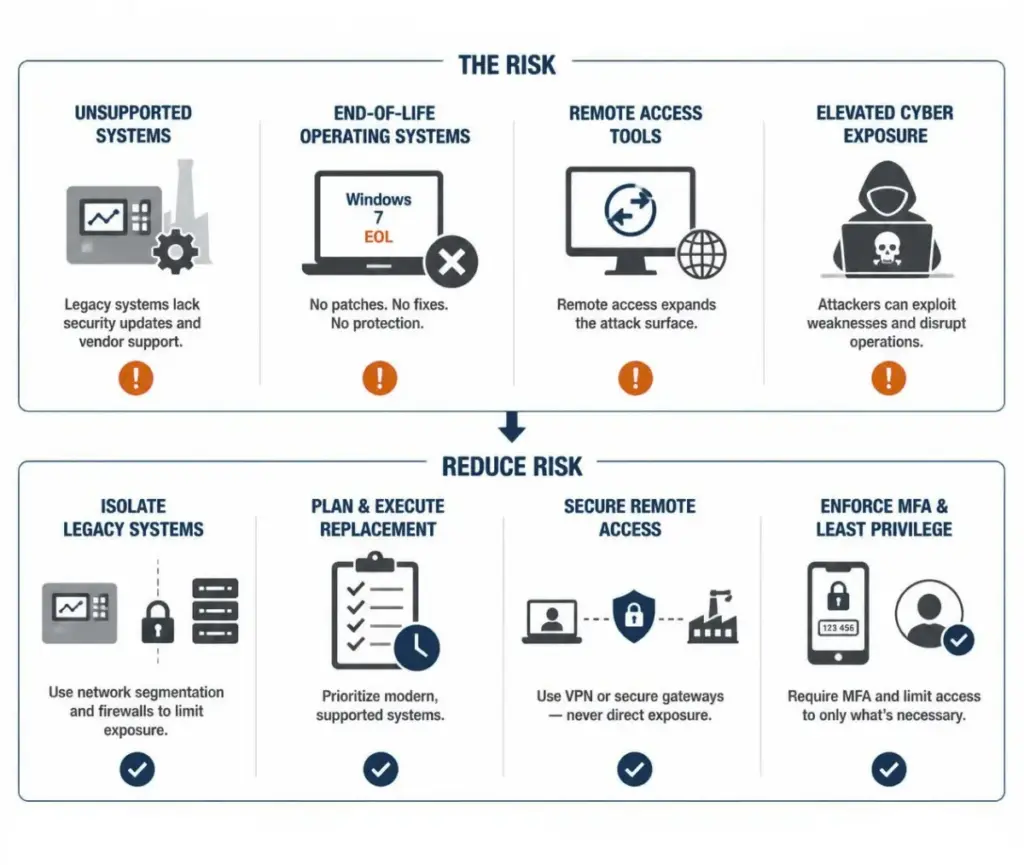
Encryption is most effective when it works with system isolation, access control, secure configuration and regular review. Together, these controls reduce the chance that sensitive data remains broadly accessible.
COMMON QUESTIONS
How Manufacturers Can Protect Sensitive Data
How can manufacturers prevent data exposure?
Manufacturers can reduce data exposure by identifying sensitive information and documenting where it is stored, used, and transmitted.
Next, teams should review encryption for endpoints, servers, databases, cloud platforms, removable media, and wireless networks. Additional controls should include MFA, least-privilege access, secure configurations, network segmentation, monitoring, and documented data-retention practices. Together, these measures help limit unauthorized access and reduce the chance that sensitive data remains readable if a device, account, or network is compromised.
How can manufacturers tell if their IT infrastructure is exposing data?
Manufacturers should begin with a data inventory and review how sensitive information moves across the environment.
Teams should identify unencrypted devices, exposed storage, misconfigured cloud services, unsecured wireless networks, weak access controls, and systems that transmit data without adequate protection. Regular vulnerability assessments, configuration reviews, access reviews, and network monitoring can help identify data-protection gaps before they lead to unauthorized access.
Why does full-disk encryption matter in manufacturing?
Full-disk encryption protects data stored on laptops, workstations, servers, and other devices. If a device is lost, stolen, or accessed without authorization, encryption can make the stored information unreadable without the required credentials or key. However, full-disk encryption protects data at rest. Manufacturers should also protect data while it is being transmitted and when it is stored in cloud platforms, databases, backups, and removable media.
How can manufacturers protect data stored in the cloud?
Manufacturers should protect cloud data by configuring storage securely, limiting access, enabling encryption, requiring MFA, monitoring account activity, and reviewing permissions regularly. In addition, teams should understand where cloud data is stored, who can access it, how it is shared, and how it is retained or deleted. Cloud providers offer security controls, but manufacturers remain responsible for configuring those controls correctly and managing access to their data.
What does encryption mean for manufacturing leaders?
For manufacturing leaders, encryption is a practical control that helps protect sensitive information from unauthorized access. It can help safeguard intellectual property, engineering data, credentials, employee information, customer records, operational data, and business communications. Leaders should ask where sensitive data exists, how it moves, who can access it, and whether encryption is applied consistently. These questions help identify gaps and prioritize improvements without disrupting essential operations.
LEADERSHIP NEXT STEPS
Strengthen Your Data Protection Strategy
Start by identifying sensitive data, reviewing encryption coverage, and closing the gaps that leave information exposed.
Accent Consulting can help your organization evaluate data-protection risks, validate encryption coverage, and build a practical roadmap for improving security.